Industries / Europe
Europe: GDPR and the EU AI Act
Document AI use and apply the controls Europe asks about.
Your role and ours differ. This page separates what the platform supports from what remains yours as controller or deployer.
The short answer
European organizations can support GDPR and EU AI Act obligations by documenting AI use cases, applying access and data controls to each request, and keeping records that show how decisions were made. SynapBridge acts as a processor under a data processing agreement. Using it does not make a deployer compliant, and applicable dates and duties depend on your role and use case.
What your reviewers ask
Questions, the control that answers each, and its status.
| Reviewer question | How the platform answers it | Status |
|---|---|---|
| Do you act as processor, and is there a DPA? | A data processing agreement is published. Your role as controller or deployer, and the transfer terms for your situation, are covered when you review the agreement with us. | Available |
| Can we document each AI use case? | A use-case registry with owners, versions and approvals supports the record-keeping and oversight conversations (Articles 12, 14 and 26 mapping in the trust center). | Beta |
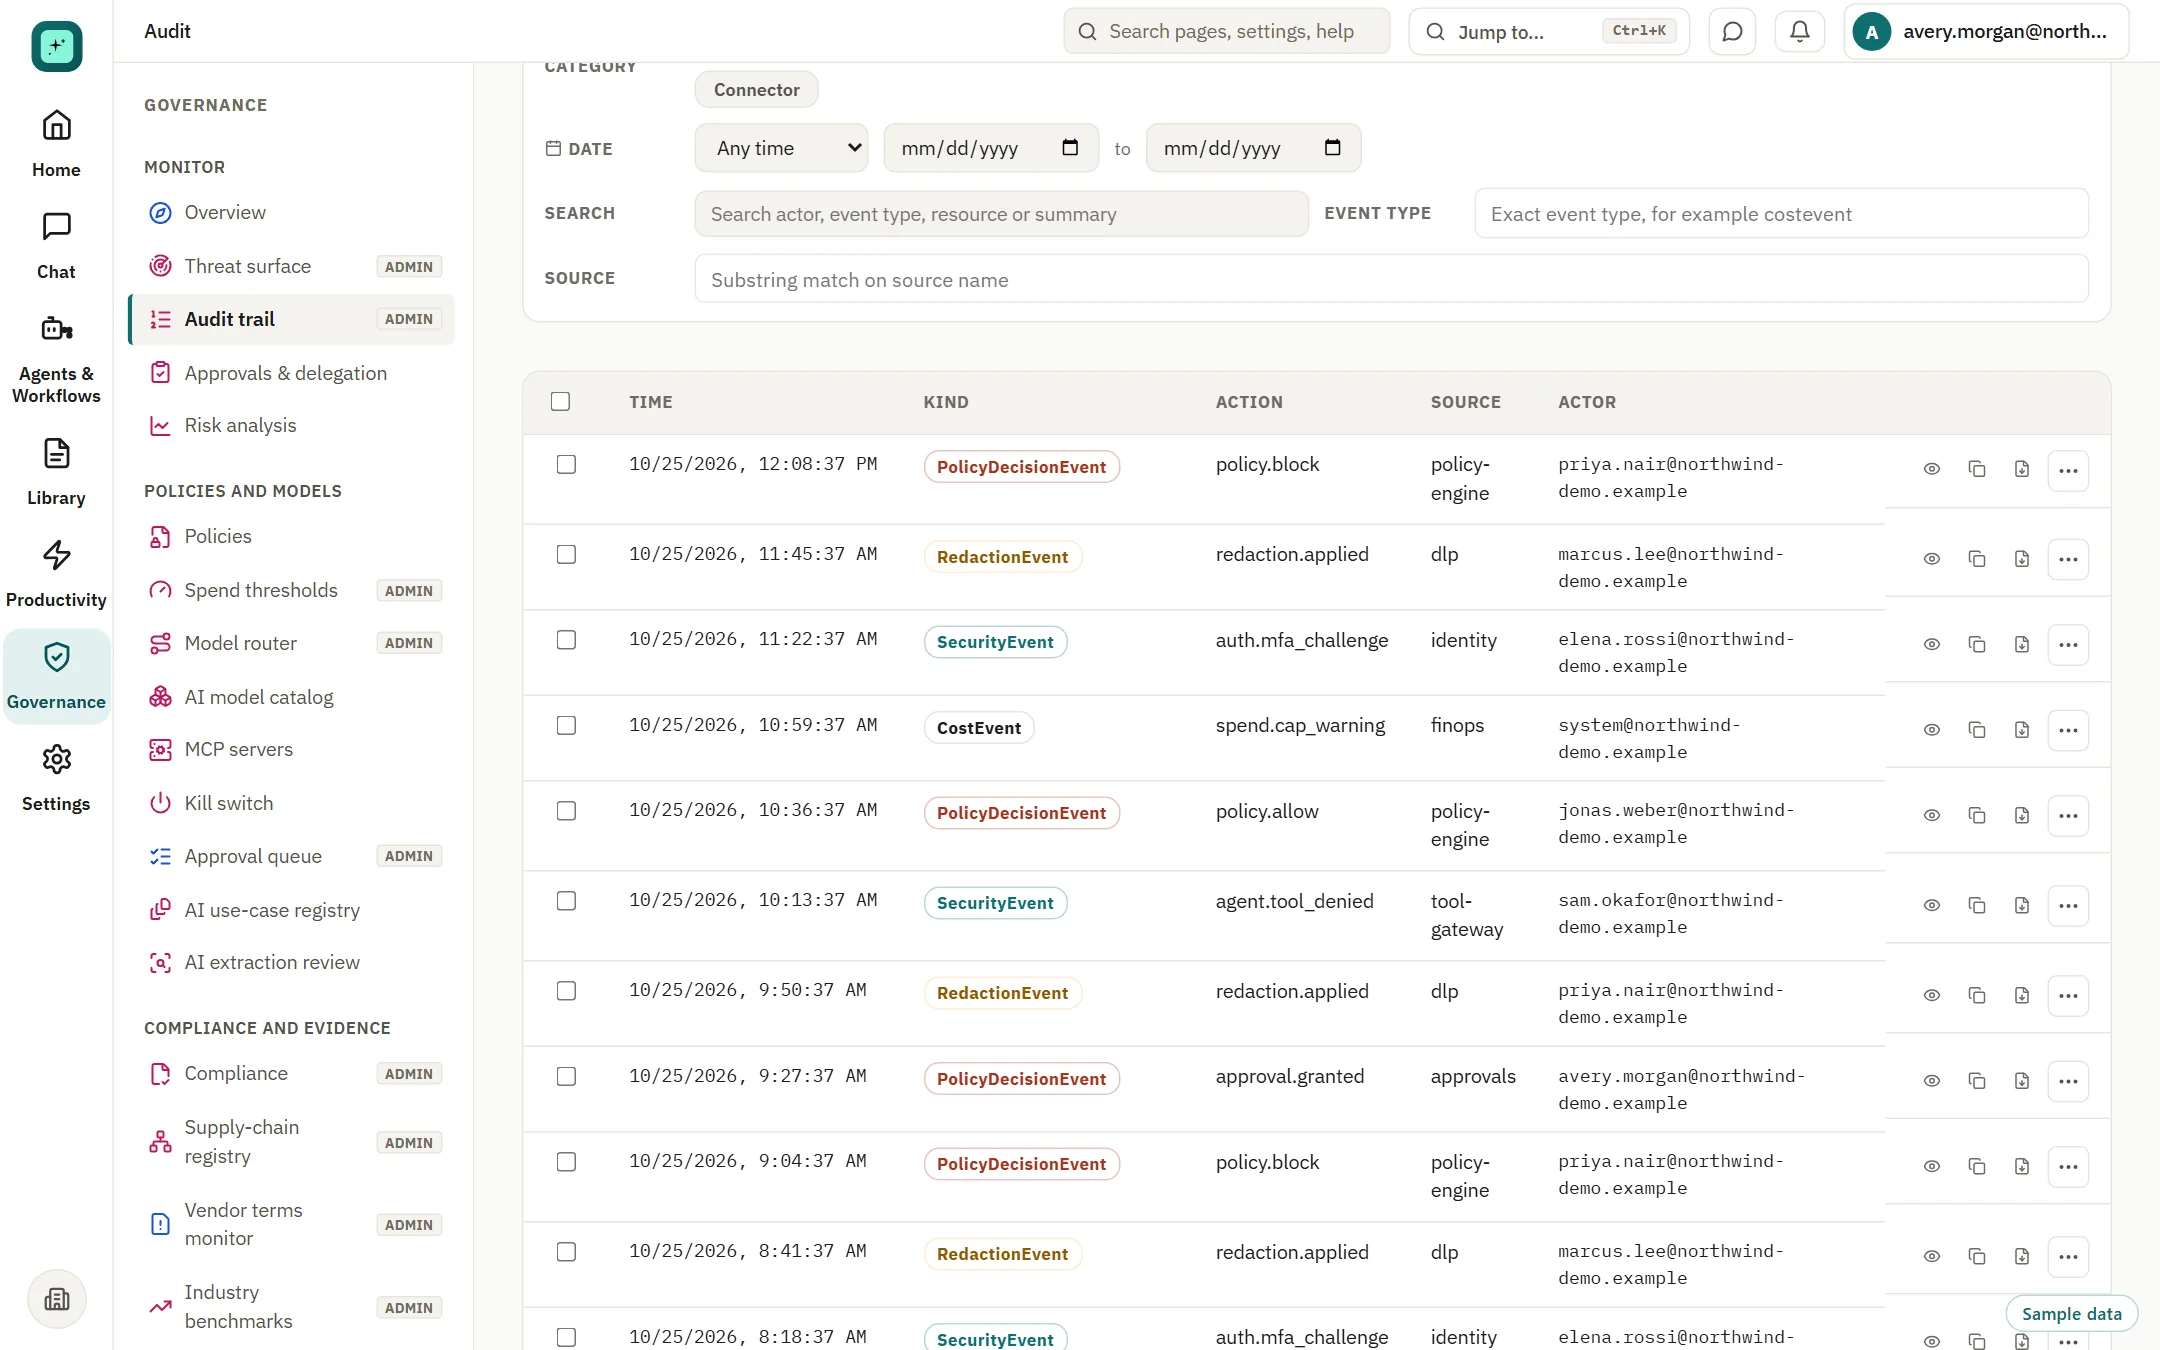
| Can we keep a record of how decisions were made? | Audit records carry the policy version, and can be searched, exported and streamed (streaming in Beta). | Available |
| Can we route by where data is processed? | Residency routing where a policy is active. A logged operational override exists for incident response and is disclosed in the trust center. Available regions are listed in the security review. | Beta |
| How do you handle data subject requests? | An access and erasure workflow is available in Beta. Ask for the current scope in a review. | Beta |
| Which transparency duties apply to us? | Transparency and AI literacy duties sit with the deployer. We map platform controls, not your duties. | Available |
Controls apply to requests made through SynapBridge, on the providers you connect. Sensitive-data detection covers known patterns. Configuration and the final compliance decision stay with you.
- The EU AI Act phases in over several years and the timeline for high-risk duties has been revised. Confirm current dates for your use cases with your counsel.
- No attestation has been issued. SynapBridge is architected to align with the SOC 2 Trust Services Criteria, and ISO/IEC 27001 is a declared intent.
- Residency routing depends on an active policy and is in Beta. It is not an unconditional guarantee.
- SynapBridge does not provide legal advice or determine your risk classification.
Questions
Asked and answered.
Is SynapBridge EU AI Act ready?
We publish a mapping of platform controls to the Act's obligations, with status for each row. That is a mapping, not a claim of readiness or compliance.
Is my data processed in the EU?
That depends on your residency policy and the providers you connect. Ask for the available regions and the current scope of enforcement in a review.
Do you have an EU representative?
Ask in a review; we will answer in writing.
Plan an evaluation with your reviewers.
Bring the questions above. The trust center answers most of them without a call.