Platform / Governance
Governance
Rules that run on every request, and a record that they ran.
Set data, model and spend rules once. SynapBridge applies them to requests made through the platform and writes the decision down.
Watch it
A request, governed.
Recorded in the product on a fictional tenant with sample data. Captioned and silent, so they play anywhere, including in a meeting.
Read the transcript
- Compare: one prompt, several models, one view. Every answer shows its latency and cost.
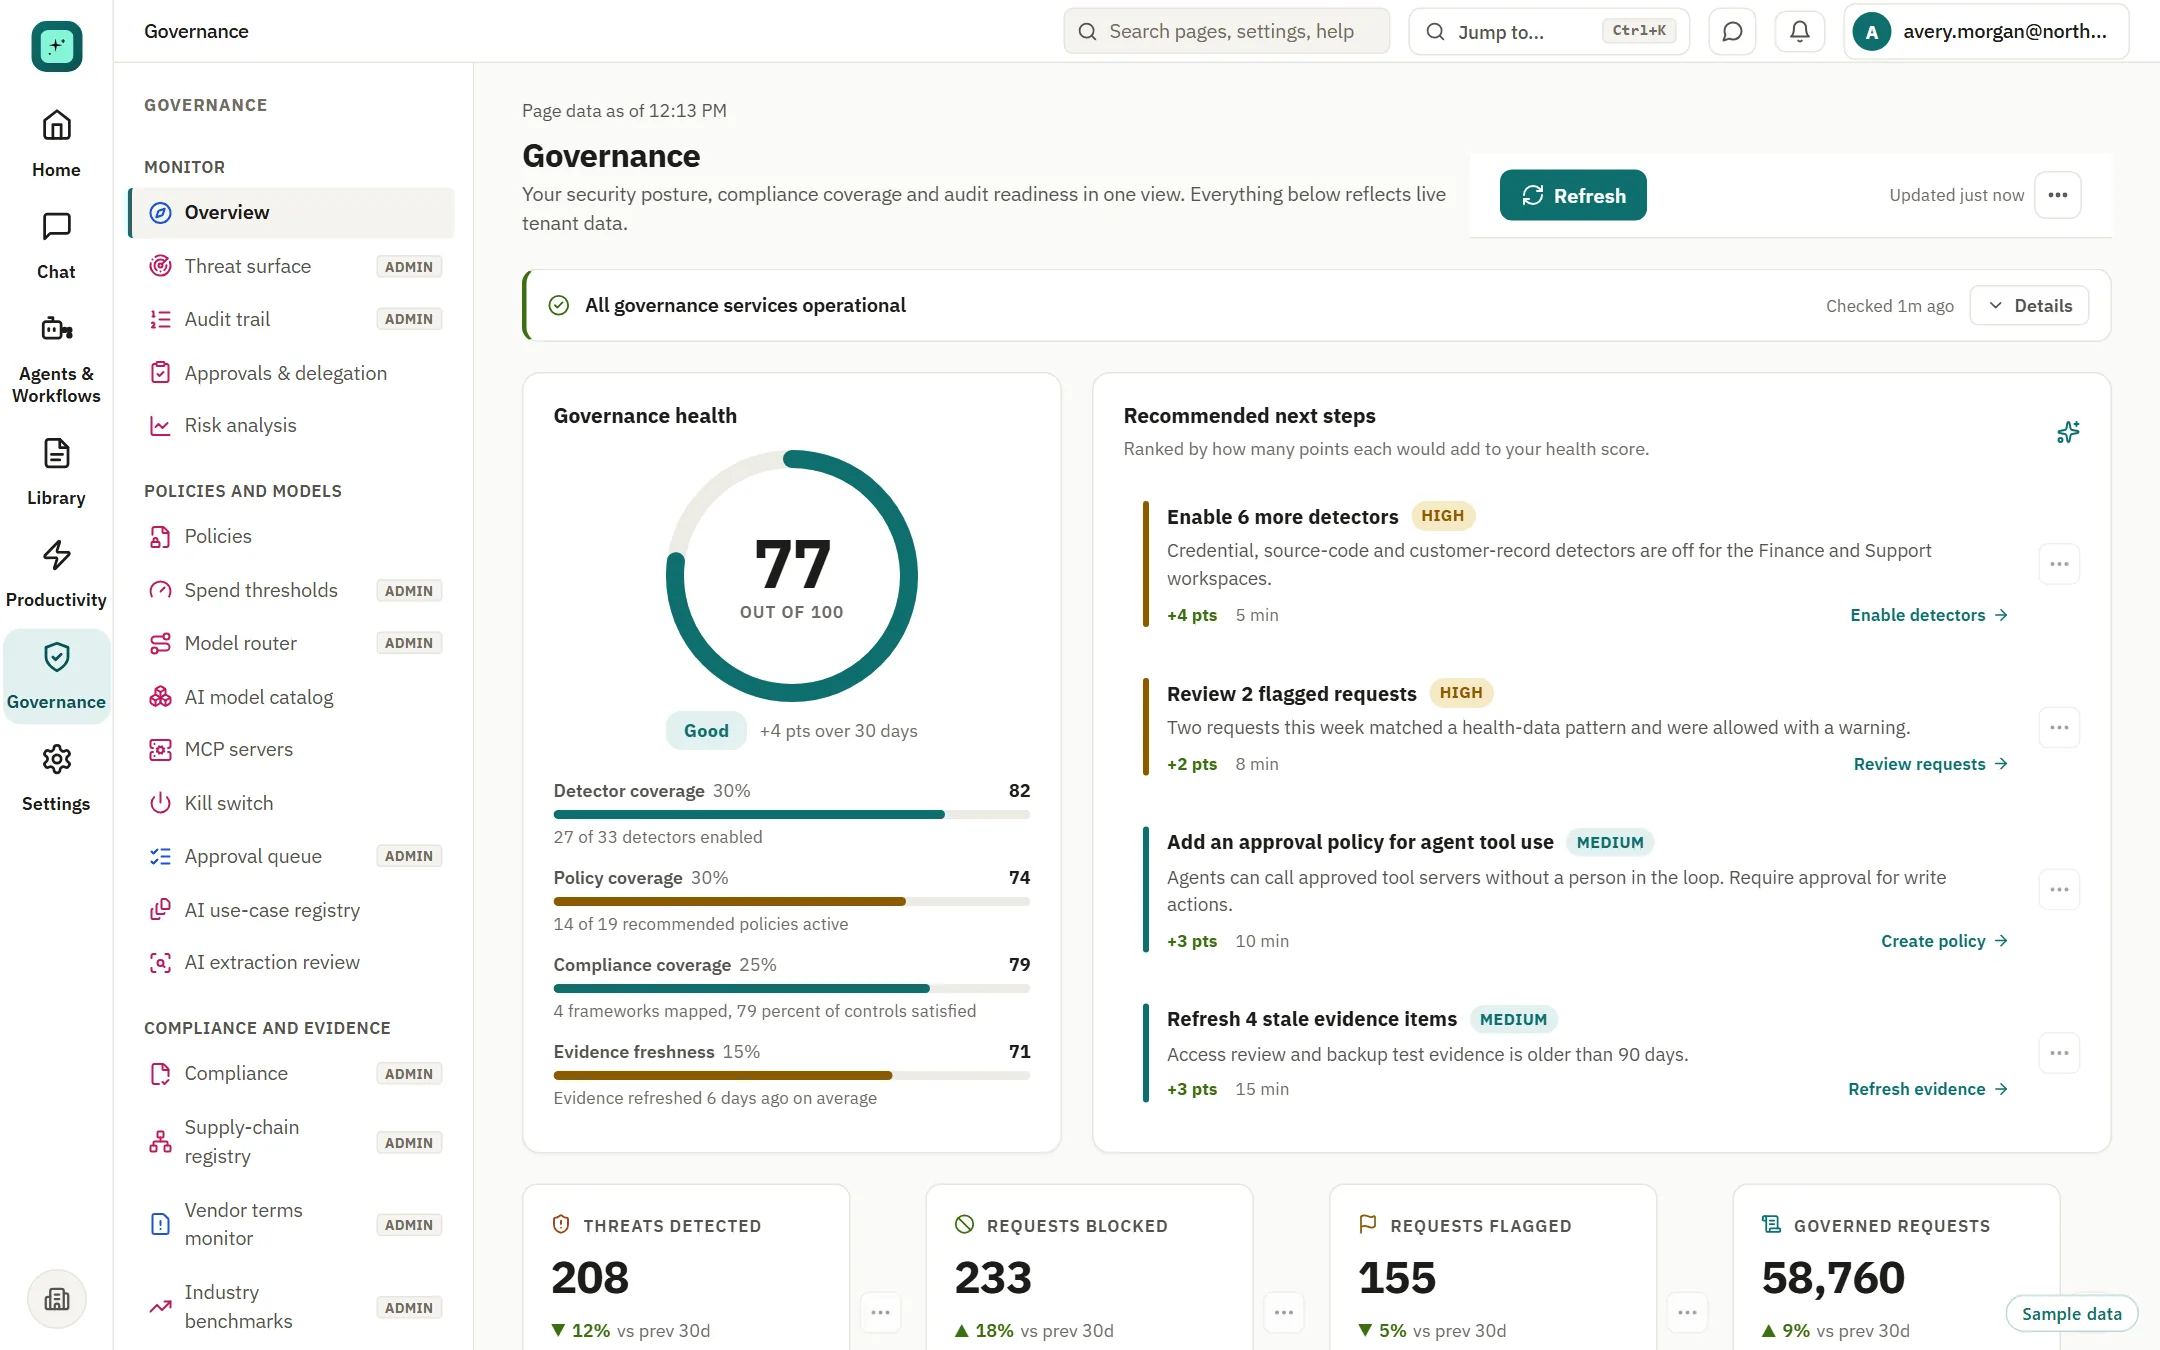
- Control: every governed request is checked against the active policy. One score, with next steps ranked by the points each adds.
- Evidence: each decision is written down with the policy version.
What runs on a request
Six checks, applied to every governed request.
Each check applies across every provider behind SynapBridge, so one rule set covers Claude, GPT, Gemini and the rest alike.
Sensitive-data pre-check
Looks for known patterns, such as health, personal and credential data, before a request leaves for a provider.
Injection screening
Screens requests for known prompt-injection patterns.
Model entitlements
Decides which people and teams may use which models, for which data classes.
Content policy
Applies your content rules, with the reason shown to the person.
Spend caps
Checks a cap at request time and warns the owner early. A check, not a hard stop.
Residency routing Beta
Routes by residency requirement where a policy is active. A logged operational override exists for incident response and is disclosed in the trust center.
Policies and simulator
Model the impact of a rule on past events.
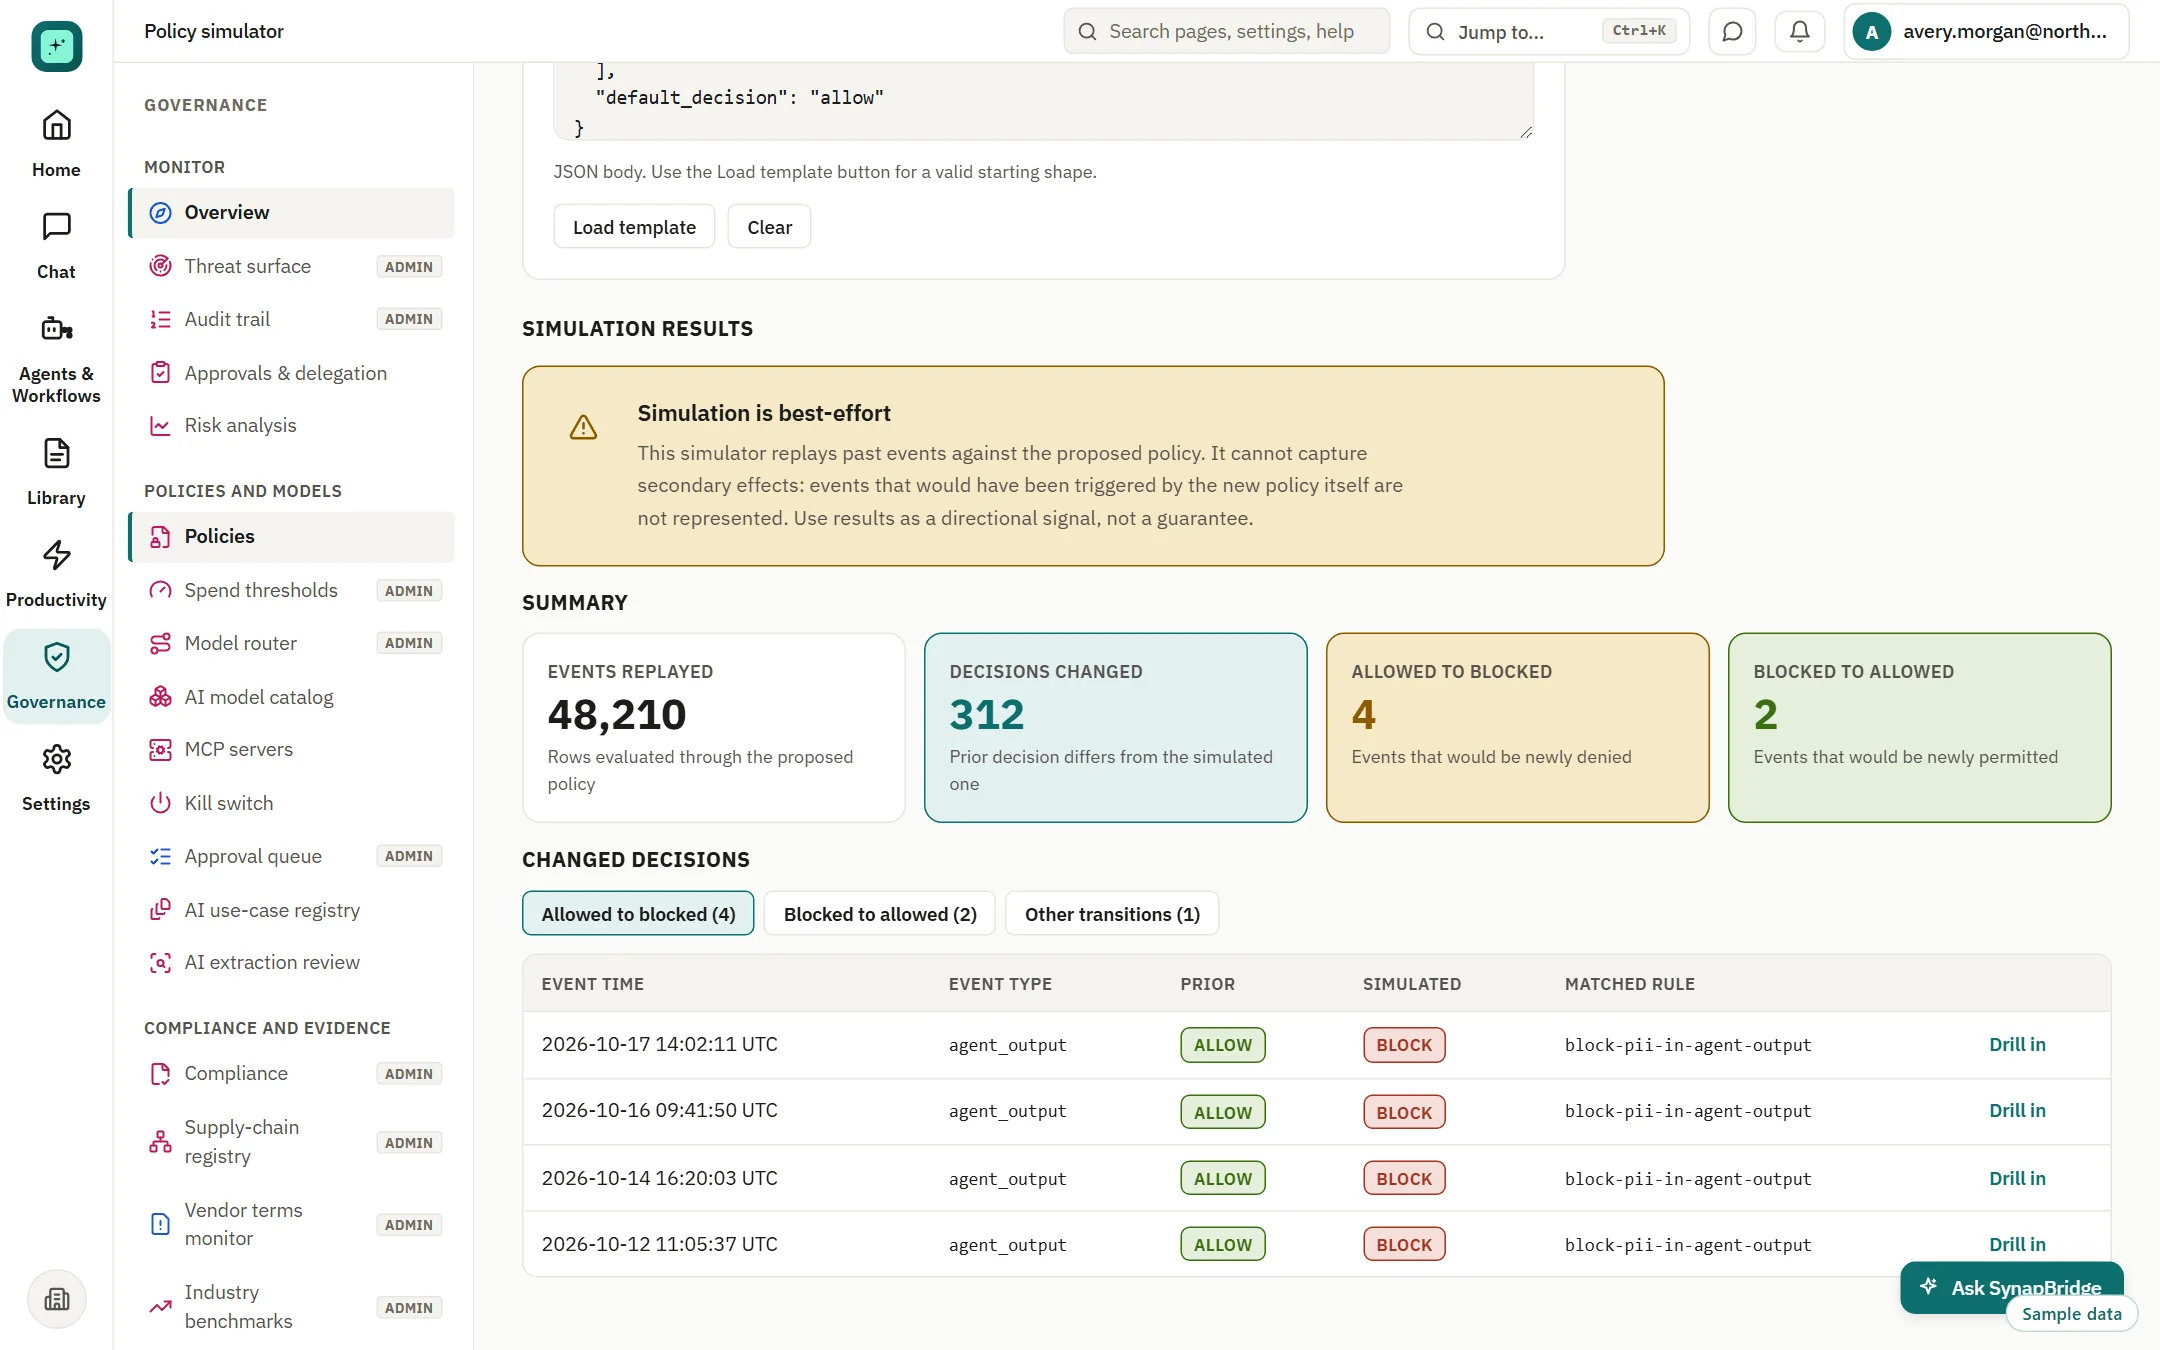
Policies are versioned with an owner, and changes go through approval. The simulator replays past events against a proposed rule set and shows what would change. Simulated rule sets are proposals and do not change live behavior today.
- Allowed-to-blocked and blocked-to-allowed, listed
- Diff and rollback between versions
- A kill switch for fast stops, with the decision recorded
Approvals and registry
Every high-impact change has an owner and a decision.
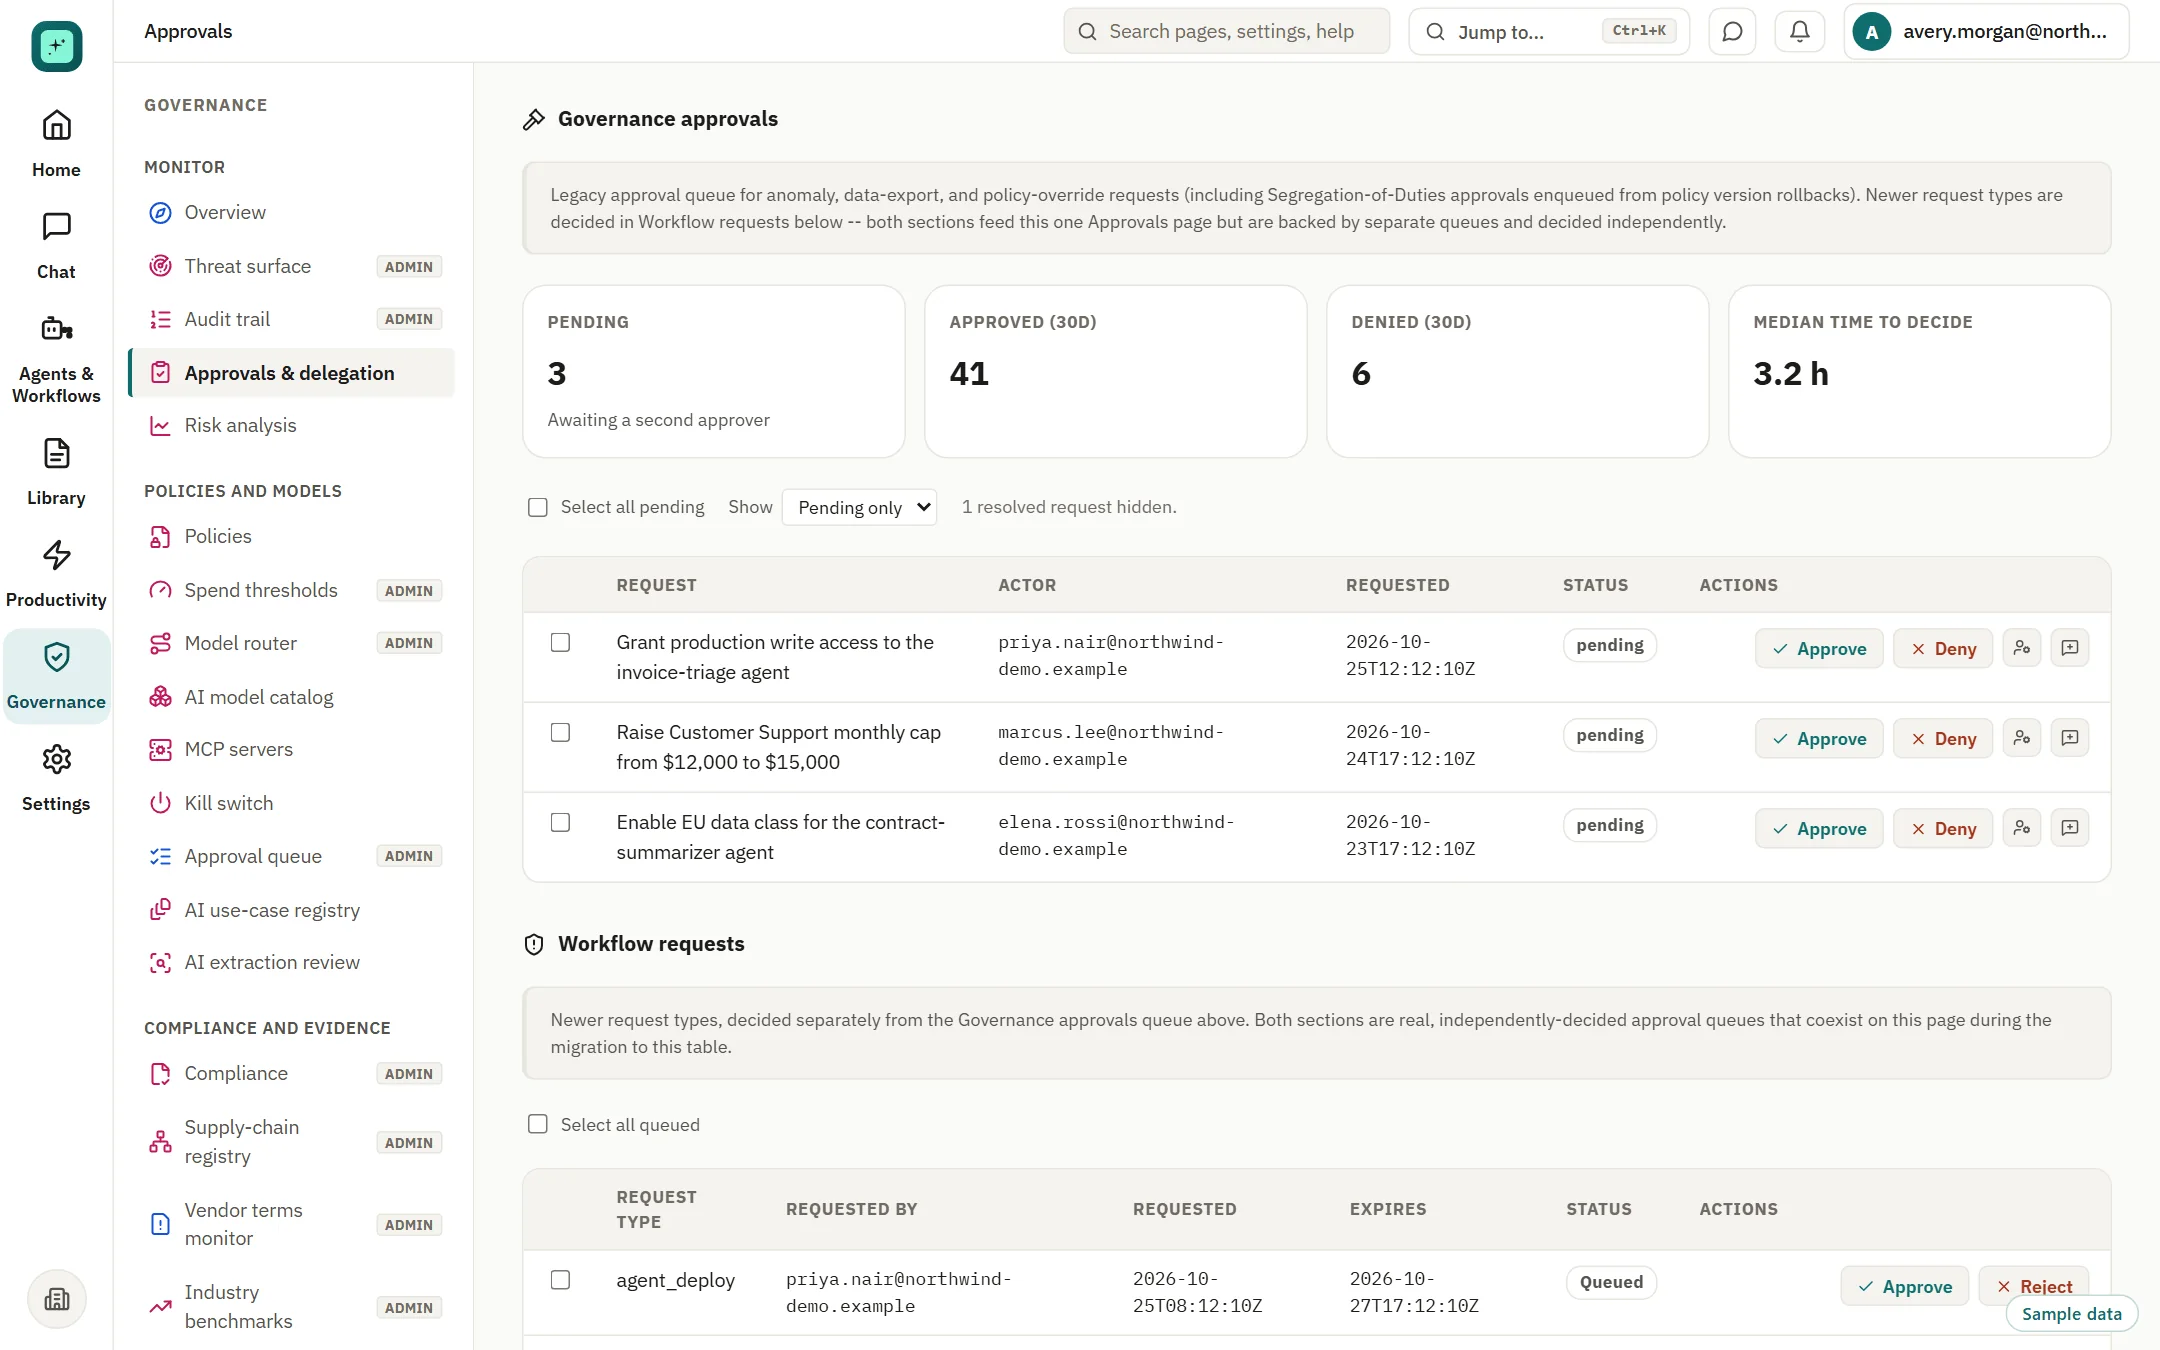
Approve, deny or reassign from one queue. A use-case registry gives every AI use a named owner.
- Delegations for planned absence
- Two-person approvals for high-impact changes
- Approvals are in Beta
Evidence
A record you can search, export and stream.
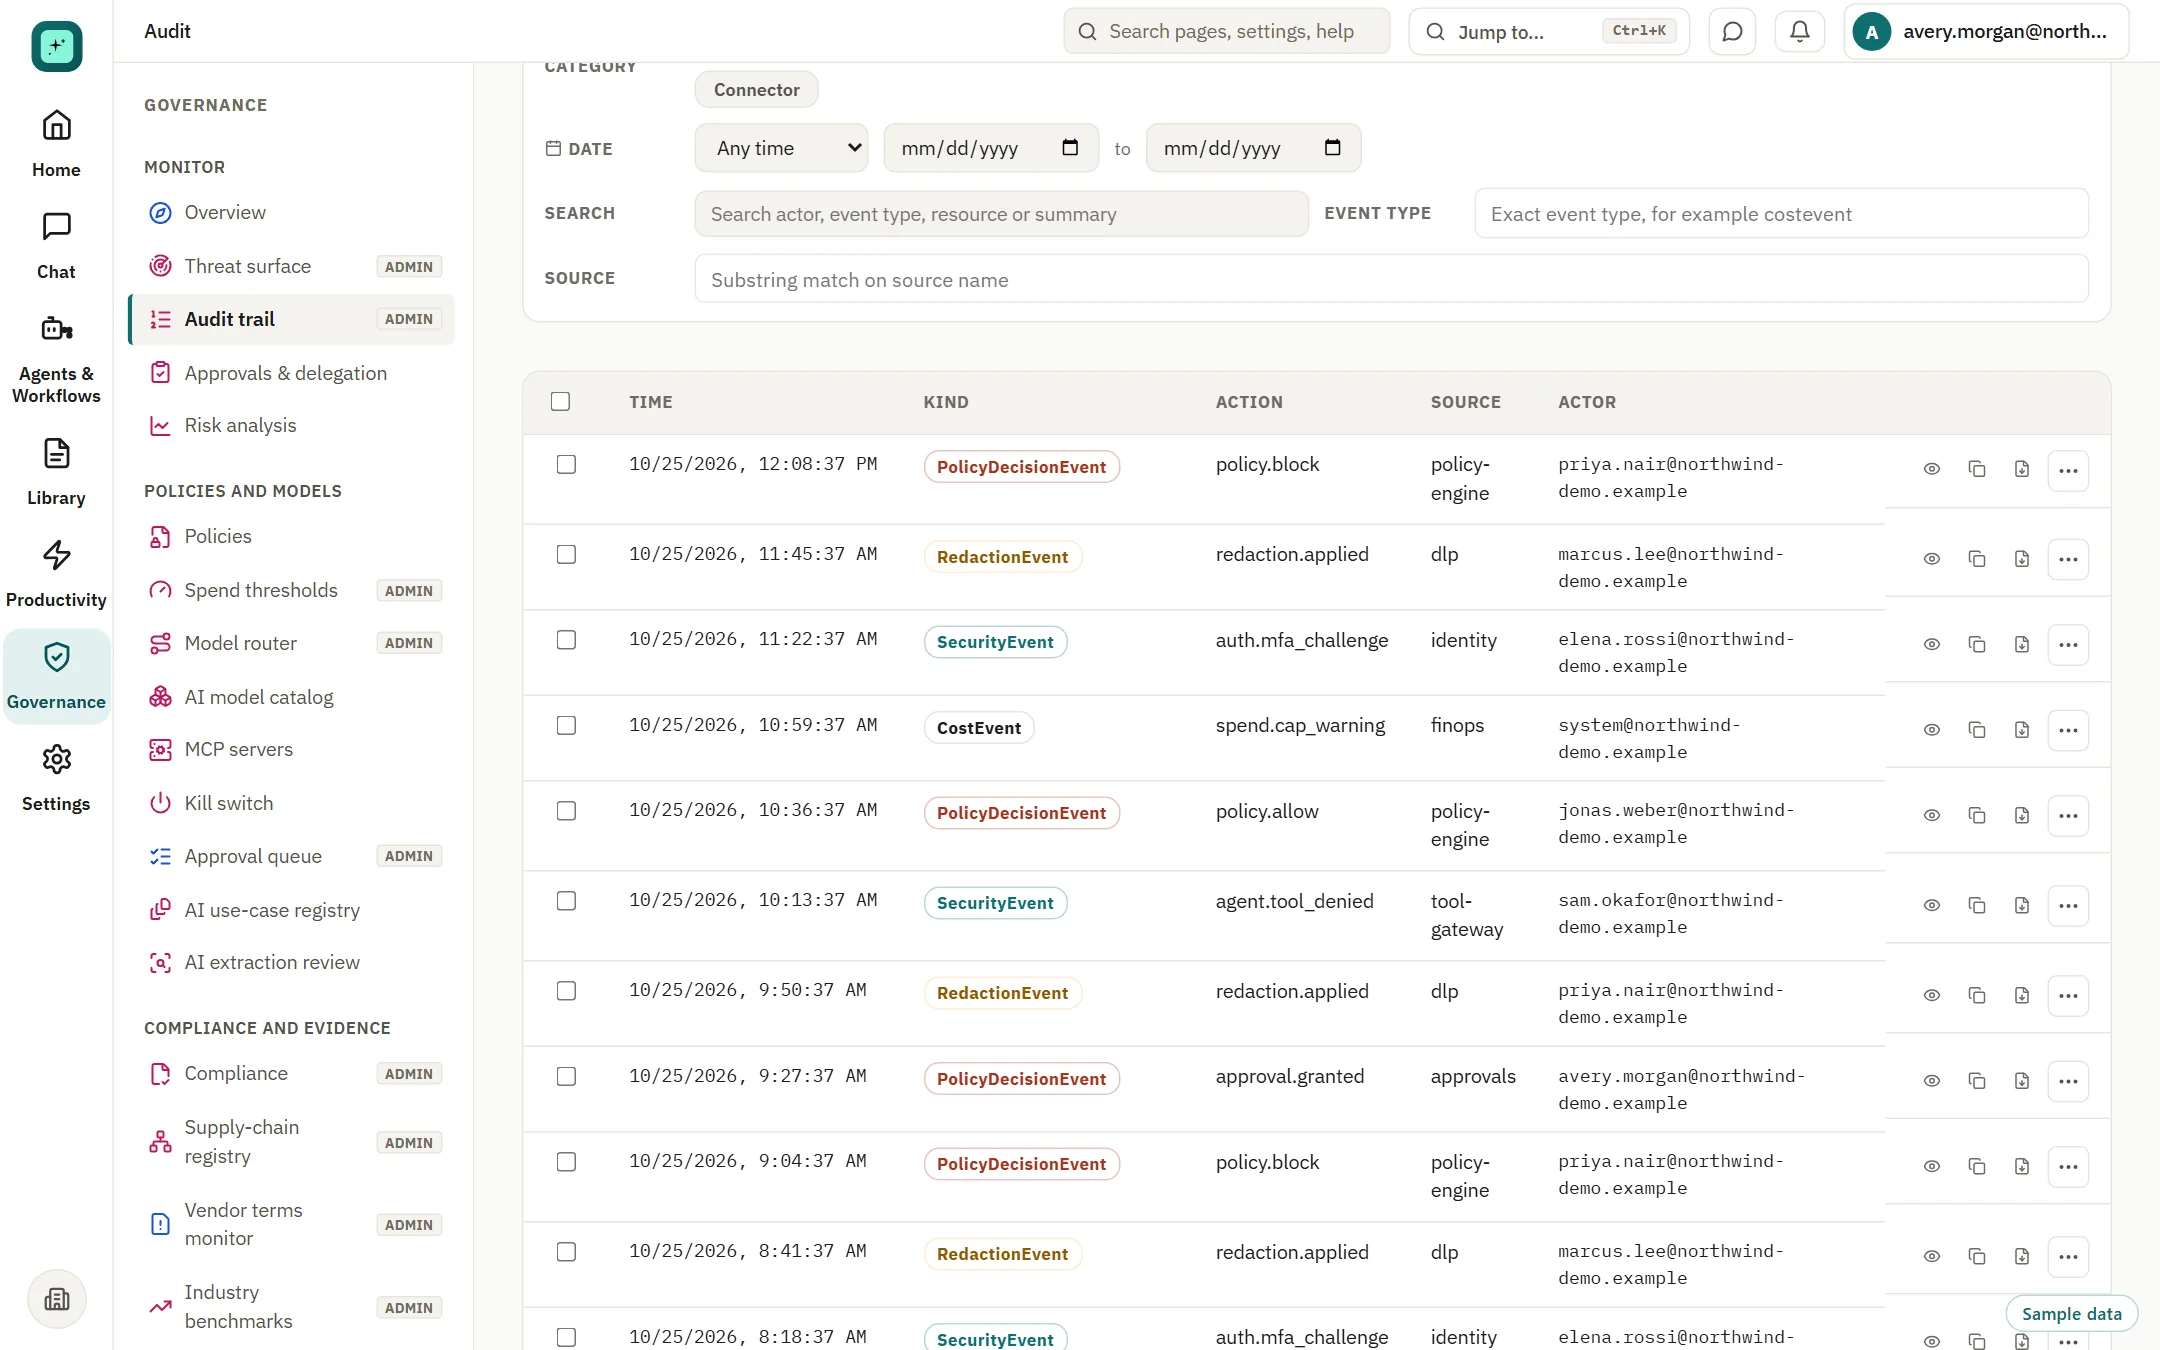
Each governed request and admin action writes a record that carries the policy version. Export it, or stream it to your SIEM.
- Searchable audit trail
- Policy version recorded with each decision
- SIEM streaming and BI export Beta
Questions
Governance, answered directly.
Which checks run on every request?
A sensitive-data pre-check, injection screening, model entitlements, content policy and spend caps. Residency routing applies where a residency policy is active.
Can a user bypass a rule?
Not inside SynapBridge. Requests made through it are checked against the active policy. Usage in other tools is outside scope unless you connect it.
What is in Beta?
Approvals, SIEM streaming, agents and tool servers, and residency routing. Behavior and limits may change; ask for the current status in a review.
Where are audit records kept?
In your workspace, searchable in the app, with export to your SIEM and BI tools.
Does a block show a reason?
Yes. The person sees the reason and the approved alternatives.
See the controls on your own providers.
Book a security review with the people who built it.