Industries / Financial services
Financial services
Show examiners how AI-assisted work is supervised.
Records, supervision and third-party oversight apply to AI the same way they apply to other tools. These pages start from the exam question.
The short answer
Financial firms can govern AI use by controlling which models may see client data, requiring named approvals for new uses, and keeping a searchable decision record that exports to the archive and SIEM tools they already run. SynapBridge applies this to requests made through it. Whether a record meets a given retention or supervision rule is for your compliance team to decide.
What your reviewers ask
Questions, the control that answers each, and its status.
| Reviewer question | How the platform answers it | Status |
|---|---|---|
| Which models may see client data? | Per-model entitlements and sensitive-data checks on each request, with a decision record for each stop. | Available |
| Can we show supervision of AI-assisted work? | A use-case registry with named owners, approvals with named reviewers, and audit records you can search and export. | Beta |
| Can records go to our archive and SIEM? | Export is available. Streaming to a SIEM is in Beta. Retention settings are yours to set against your own policy. | Available |
| How do we oversee third-party models? | One list of connected providers with status, the data processing agreement and the sub-processor register. | Available |
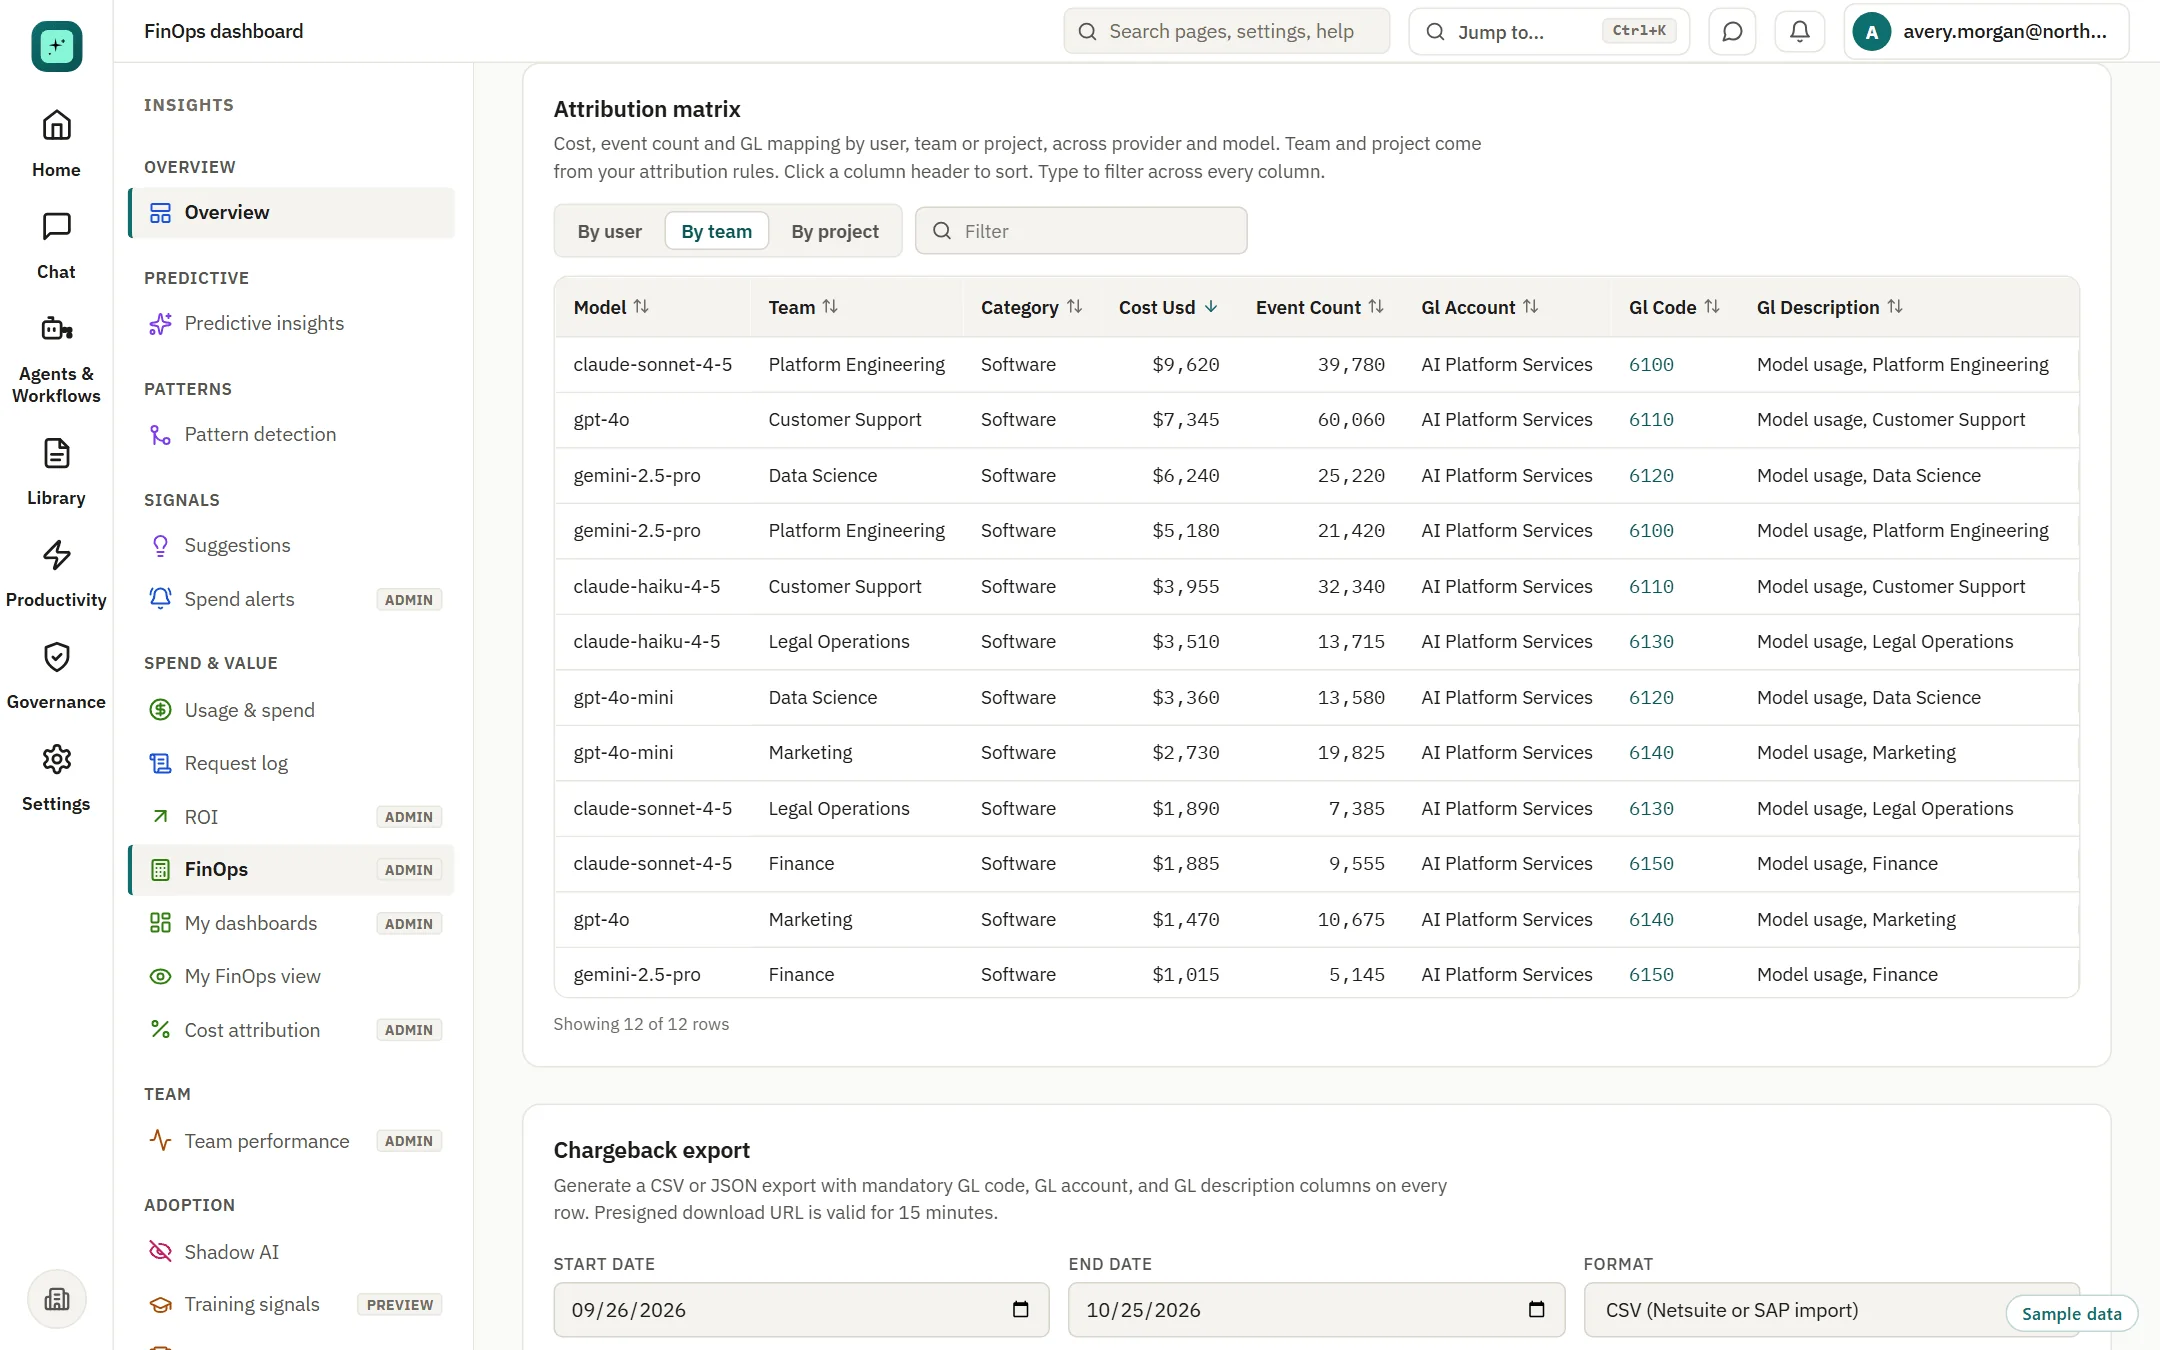
| Who owns AI spend, and can we charge it back? | A ledger across connected vendors with attribution to team and project, and a ledger code on every row. | Available |
| Can we model a policy before we change it? | Versioned policies, and a simulator that replays past events against a proposed rule set. Simulated rule sets are proposals today. | Available |
| Are agents and tool servers approved? | A registry and approval path for agents and tool servers. | Beta |
Controls apply to requests made through SynapBridge, on the providers you connect. Sensitive-data detection covers known patterns. Configuration and the final compliance decision stay with you.
- SynapBridge is not a records-retention or WORM archive and does not decide whether a record satisfies SEC, FINRA or other rules.
- No attestation has been issued. SynapBridge is architected to align with the SOC 2 Trust Services Criteria, and no report exists.
- Detection covers known patterns and is not a guarantee.
- Usage in other tools is outside scope unless you connect it.
Evidence to read
Questions
Asked and answered.
Does SynapBridge satisfy SEC 17a-4?
We make no such claim. Audit records export to the archive tools you already use, and your compliance team decides whether they meet your obligations.
Is it SOC 2 attested?
No. SynapBridge is architected to align with the SOC 2 Trust Services Criteria, and no report has been issued. The trust center shows what is verified, in progress and planned.
Can we see AI spend by desk or team?
Yes, for requests made through SynapBridge on connected providers, attributed to team, project and tag.
Plan an evaluation with your reviewers.
Bring the questions above. The trust center answers most of them without a call.